Understanding the Dual Nature of AI in Cybersecurity
Artificial intelligence is reshaping cybersecurity, presenting both powerful defensive capabilities and novel attack vectors. Its integration into security operations has become critical, allowing organizations to combat the scale and sophistication of modern cyber threats more efficiently.
However, this transformative technology also arms malicious actors, necessitating a comprehensive understanding of its inherent risks. Recognizing the dual nature of AI, as both a shield and a potential weapon, is essential for security leaders.
AI's significance in cybersecurity stems from its ability to process and analyze vast volumes of data more efficiently and accurately than human capabilities allow. This enables enhanced threat intelligence, automated response mechanisms, and proactive vulnerability identification.
Security leaders recognize both sides. In the World Economic Forum's Global Cybersecurity Outlook 2026, 94% of survey respondents expected AI to be the most significant driver of change in cybersecurity, and 87% of respondents identified AI-related vulnerabilities as the fastest-growing cyber risk of 2025.
Simultaneously, attackers can weaponize the same capabilities that make AI an effective defense, leading to more sophisticated and evasive attacks, as well as new ethical dilemmas and operational challenges. A balanced perspective that weighs both the benefits and the risks is essential for building effective, adaptable cybersecurity strategies.
Traditional Cybersecurity vs. AI-Enhanced Cybersecurity
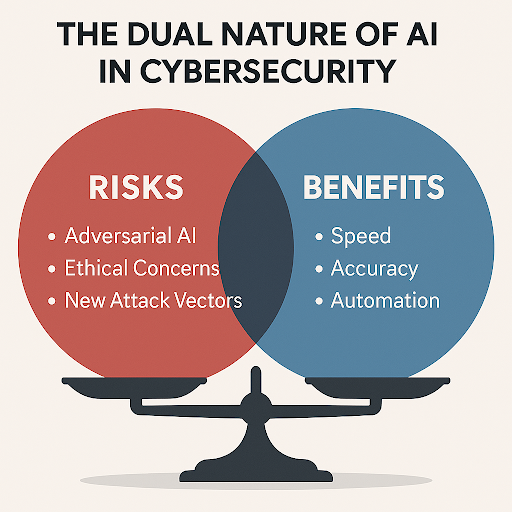
AI in Cybersecurity Pros and Cons at a Glance
The main advantages and disadvantages of AI in cybersecurity are summarized below.
Pros:
- Faster threat detection: AI flags anomalies and threats in real time or near real time.
- Analysis at scale: AI continuously analyzes data volumes that exceed human capacity.
- Automated incident response: AI triggers containment actions, such as isolating infected endpoints or blocking malicious IP addresses.
- Predictive threat intelligence: Machine learning models analyze historical attack data to anticipate emerging threats.
- Risk-based vulnerability prioritization: AI ranks vulnerabilities by context, exploitability, and asset criticality.
Cons:
- AI-powered attacks: Attackers use AI to automate campaigns, adapt malware, and create convincing deepfakes.
- Adversarial manipulation of AI models: Model poisoning and adversarial inputs can cause AI systems to miss threats or misclassify activity.
- Algorithmic bias and "black box" opacity: Biased training data and opaque decisions complicate auditing and accountability.
- Over-reliance and reduced human oversight: Over-automated teams may miss novel attacks that AI has not been trained to recognize.
- Data privacy and compliance exposure: AI systems process sensitive data and must comply with evolving data protection laws.
Benefits of AI in Cybersecurity
Artificial intelligence offers substantial advantages in enhancing an organization's cybersecurity posture. Its analytical power transforms how security teams identify, respond to, and prevent cyber threats.
Enhanced Threat Detection and Analysis
AI excels at sifting through vast quantities of data to uncover subtle indicators of compromise that human analysts might miss. This capability enables earlier detection and a more comprehensive understanding of threat landscapes.
Real-Time Anomaly Detection
AI algorithms continuously monitor network traffic, system logs, and user behavior for deviations from established baselines. They can pinpoint unusual activities—like unauthorized access attempts or data exfiltration—in real time. This immediate flagging allows security teams to investigate and mitigate potential breaches before they escalate.
Predictive Threat Intelligence
Machine learning models analyze historical attack data and current threat intelligence feeds to identify emerging patterns and anticipate future attacks. This predictive capability enables organizations to strengthen their defenses against likely threats proactively. It shifts the security paradigm from reactive to anticipatory, bolstering overall resilience.
Automated Incident Response and Orchestration
Beyond detection, AI plays a pivotal role in automating the complex and time-sensitive tasks involved in incident response. This automation significantly reduces response times and minimizes the impact of cyber attacks.
Rapid Containment and Remediation
AI-driven systems can automatically trigger response actions upon detecting a threat, such as isolating infected endpoints or blocking malicious IP addresses. This immediate containment helps stop threats from spreading across the network, limiting damage and accelerating recovery. Automated remediation tasks further streamline the process.
Security Automation and Workflow Optimization
AI integrates with Security Orchestration, Automation, and Response (SOAR) platforms to automate repetitive security tasks and workflows. This includes functions like incident triage, data enrichment, and playbook execution. Automating these processes frees security analysts to focus on more complex investigations and strategic initiatives.
Vulnerability Management and Risk Assessment
AI significantly improves an organization's ability to identify and address vulnerabilities before attackers can exploit them. It moves beyond traditional scanning to provide more intelligent insights into potential weaknesses.
Proactive Vulnerability Identification
AI algorithms can analyze code, network configurations, and system architectures to identify potential vulnerabilities and misconfigurations. They draw on large databases of known vulnerabilities and exploit techniques to pinpoint weaknesses proactively. This proactive stance helps prevent attacks by addressing security gaps early.
Prioritized Risk Remediation
AI can assess the context and potential impact of identified vulnerabilities, prioritizing them based on factors like exploitability and asset criticality. This intelligent prioritization ensures that security teams focus their efforts on the most significant risks. It optimizes resource allocation for maximum security improvement.
Improved Behavioral Analytics and UEBA
Understanding normal user and entity behavior is crucial for detecting insider threats and compromised accounts. AI-powered behavioral analytics provide deep insights into these patterns.
Insider Threat Detection
AI-driven user and entity behavior analytics (UEBA) solutions establish baselines for individual user and entity behavior. They flag deviations such as unusual access patterns, data downloads, or login times that may indicate malicious insider activity. This enables early detection of potentially harmful actions by employees or trusted partners.
Compromised Account Identification
By continuously analyzing login attempts, access patterns, and resource utilization, AI can identify anomalies indicative of compromised user accounts. For example, logins from unusual geographical locations or multiple failed login attempts followed by a successful one can trigger alerts. These insights enable the quick identification and remediation of hijacked accounts, thereby preventing further damage.
Risks and Challenges of AI in Cybersecurity
While AI offers substantial benefits, its adoption in cybersecurity also introduces new complexities and potential vulnerabilities. Security professionals must understand and address these inherent challenges.
Emerging AI-powered Attack Vectors
Malicious actors can weaponize the same AI capabilities that enhance defenses, leading to more sophisticated and evasive attacks. The arms race between offensive and defensive AI is a significant concern.
Adversarial AI and Model Poisoning
Attackers can manipulate AI models by injecting malicious data during training—known as model poisoning—or by crafting inputs that cause a trained model to misclassify data—adversarial attacks. This can lead to AI systems failing to detect threats or, worse, classifying legitimate activity as malicious. Such attacks undermine the reliability of AI-driven security tools.
The National Institute of Standards and Technology's adversarial machine learning taxonomy (NIST AI 100-2e2025) groups these threats into evasion, poisoning and privacy attacks against predictive AI systems, and adds misuse attacks for generative AI systems. Security teams can use this taxonomy to map which attack classes apply to each AI model they deploy.
Prompt Injection and AI Agent Security Risks
Generative AI applications and autonomous agents introduce additional risks when they process untrusted content or interact with external tools.
A prompt injection attack attempts to influence an AI system through malicious instructions embedded in content such as documents, websites, messages or tool responses.
In an inadequately protected system, these instructions may cause an AI application to disregard intended restrictions or perform unauthorized actions. AI agents can increase the potential consequences because they may have access to files, APIs, credentials or business workflows.
Example: An AI assistant retrieves a document containing malicious instructions that attempt to persuade the assistant to disclose confidential information through an external tool. Mitigations include enforcing permissions outside the model, limiting tool access, validating actions and treating external content as untrusted.
Automated Malicious Tools and Campaigns
AI can automate the creation and execution of highly personalized and effective cyber attacks. This includes autonomous malware that adapts to defenses, self-propagating worms, and sophisticated scanning tools. Unit 42 attributes part of the speed-up in attacks to AI: in its 2026 Global Incident Response Report, the fastest 25% of intrusions reached data exfiltration in 1.2 hours, down from 4.8 hours the year before. Unit 42 describes AI as "a massive friction reducer" for attackers, though it notes adversaries are still early in adopting AI-enabled tradecraft. In an earlier Unit 42 simulation, an AI-assisted attack reduced time-to-exfiltration to 25 minutes.
Sophisticated Phishing and Deepfake Social Engineering
Generative AI can create highly convincing deepfakes—realistic but fake images, audio, or video—for use in advanced phishing and social engineering campaigns. These AI-generated fakes can convincingly impersonate executives or trusted individuals, making them harder for employees to spot.
The FBI's warning on generative AI fraud reports that criminals use AI-generated text, images, cloned voices and video to make fraud schemes more believable and to run them at larger scale. In ISC2's 2025 workforce study, 40% of surveyed practitioners said they had experienced AI-optimized social engineering attacks.
Agentic AI Risks
Agentic AI systems plan tasks, call tools, and take actions with limited human direction. As a result, a compromised or misconfigured agent can act at machine speed with real permissions. In their joint agentic AI guidance, the Cybersecurity and Infrastructure Security Agency (CISA), the National Security Agency (NSA), the Australian Signals Directorate's Australian Cyber Security Centre (ASD's ACSC), and partners in Canada, New Zealand, and the UK identify five risk categories:
- Privilege risks from over-scoped access.
- Design and configuration risks.
- Behavior risks when agents act in unintended ways.
- Structural risks from interconnected agents and tools.
- Accountability risks when actions are hard to trace.
Understanding these agentic AI security risks helps security teams decide which controls to apply before agents reach production.
Ethical and Trust Concerns
The pervasive nature of AI raises significant ethical considerations, particularly regarding fairness, privacy, and accountability. Ensuring the ethical deployment of AI is critical for maintaining trust and avoiding unintended negative consequences.
Algorithmic Bias and Discriminatory Outcomes
AI models learn from the data they are trained on. If this data contains biases—intentional or unintentional—the AI system can perpetuate or even amplify those biases. In a cybersecurity context, this could result in certain user groups being unfairly flagged or legitimate activities being misidentified as threats due to biased historical data. Addressing data bias is essential for equitable security.
Accountability, Transparency, and "Black Box" Issues
The complex, "black box" nature of some advanced AI models can make it difficult to understand how they arrive at specific decisions. This lack of transparency poses challenges for auditing, explaining security incidents, and establishing accountability when AI systems make errors or contribute to breaches. Ensuring explainable AI (XAI) is crucial for establishing trust and ensuring legal compliance.
Operational and Human Capital Challenges
An excessive reliance on AI without adequate human oversight or expertise can create new vulnerabilities. The human element remains indispensable for effective cybersecurity.
Over-Reliance and Reduced Human Oversight
Over-automation can lead to a reduction in human vigilance and critical thinking. If security teams become too dependent on AI to identify all threats, they may miss novel or subtle attack methods that the AI has not been trained to recognize. Maintaining human oversight and the ability to intervene are crucial for comprehensive security.
Talent Shortages and Skill Gaps
The rapid advancement of AI technology has created a significant demand for cybersecurity professionals with expertise in AI, machine learning, and data science. A shortage of skilled personnel capable of developing, deploying, and managing AI-driven security solutions creates a critical gap.
The 2025 ISC2 Cybersecurity Workforce Study found that 59% of surveyed practitioners report critical or significant skills needs, up from 44% in 2024, and respondents ranked AI as the most pressing skills need at 41%. This shortage hinders the effective adoption and management of AI.
Data Privacy and Compliance Implications
AI systems often require access to vast amounts of sensitive data. This data consumption introduces significant privacy and compliance challenges.
Handling Sensitive Data at Scale
AI models analyzing network traffic, user behavior, and threat intelligence often process sensitive personal and organizational data. Ensuring the secure handling, storage, and anonymization of this data is essential to prevent privacy breaches. Organizations must implement resilient data governance strategies.
Navigating Evolving Regulatory Landscapes
The rapid evolution of AI technology often outpaces the development of regulatory frameworks. Organizations deploying AI in cybersecurity must navigate a complex and evolving landscape of data protection laws and industry-specific regulations.
The EU AI Act shows how quickly obligations are arriving. According to the European Commission's EU AI Act application timeline, prohibitions on certain AI practices have applied since February 2, 2025, and general-purpose AI obligations since August 2, 2025.
Under the Digital Omnibus, which entered into force on July 27, 2026, high-risk system rules apply from December 2, 2027, or August 2, 2028, for AI embedded in products. Non-compliance can lead to severe penalties and reputational damage.
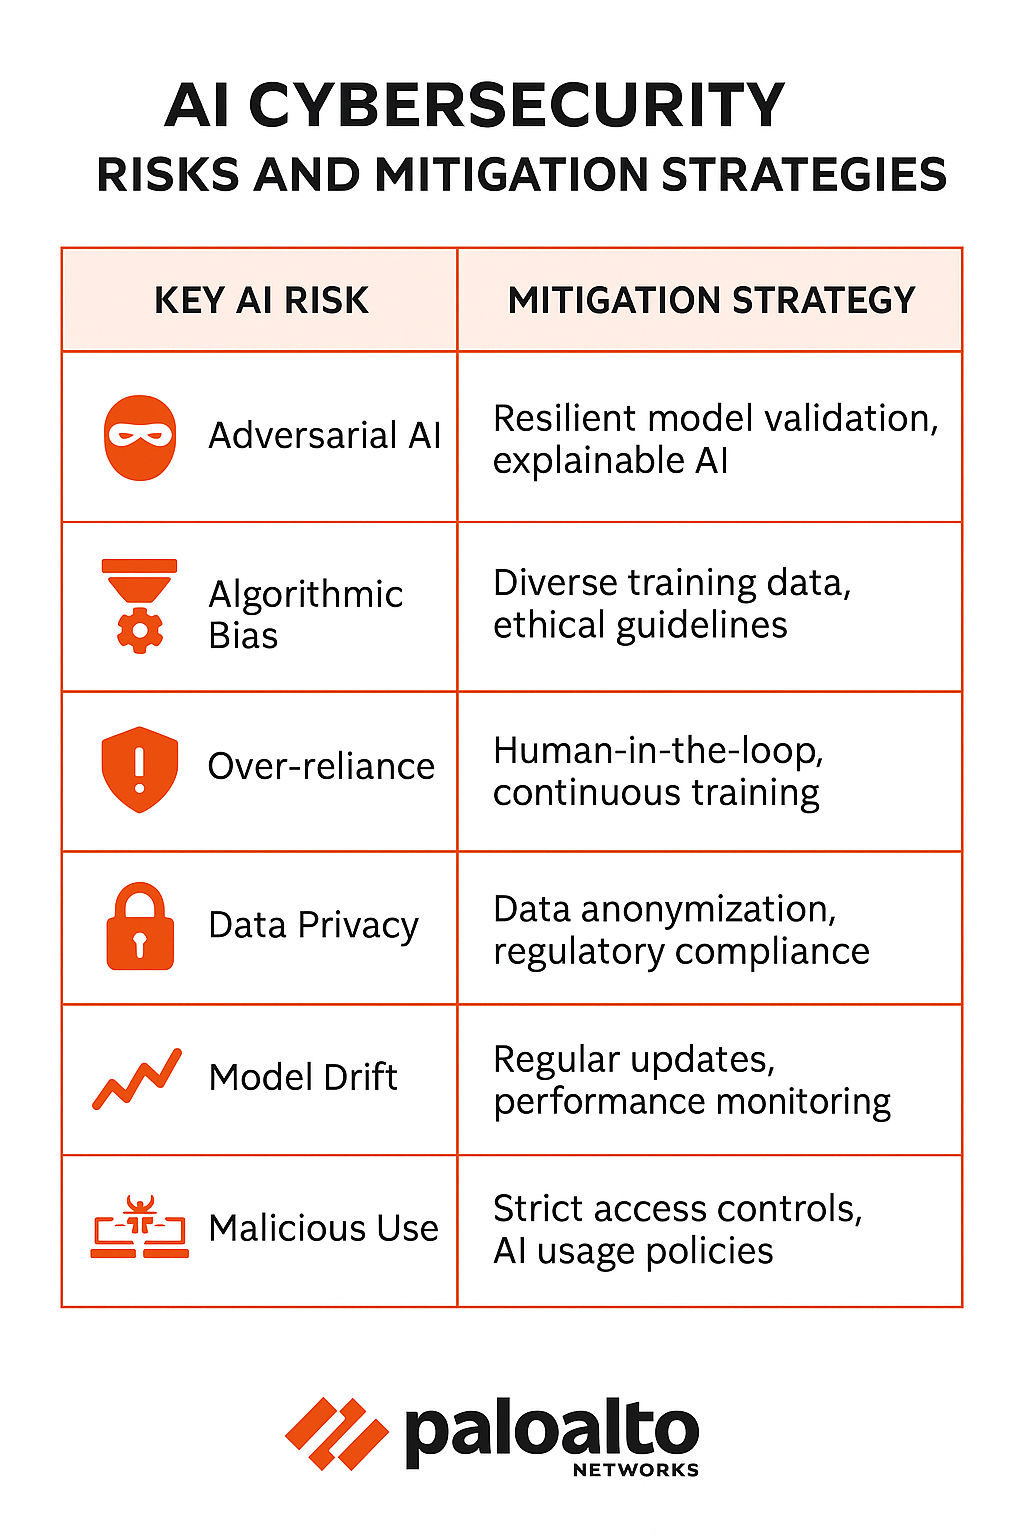
Mitigating Risks and Maximizing Benefits: Strategic Implementation
Successfully integrating AI into a cybersecurity framework requires careful planning, strong development practices, and a commitment to responsible deployment. This involves both technical implementation and strategic oversight.
Developing a Secure AI Framework
A comprehensive framework is essential to ensure that AI systems themselves are secure and contribute effectively to overall security. This framework must cover the entire lifecycle of AI models. Organizations do not need to start from scratch.
The voluntary NIST AI Risk Management Framework and its Generative AI Profile provide a structure for mapping, measuring and managing AI risk, and NIST is currently revising AI RMF 1.0. NIST also released a preliminary draft Cyber AI Profile in December 2025. It organizes AI security around three focus areas: securing AI system components, conducting AI-enabled cyber defense and thwarting AI-enabled attacks.
Integrating Security into the AI Development Lifecycle
Integrating security practices throughout the AI development lifecycle—from data collection and model training to deployment and maintenance—is critical.
This involves implementing secure coding practices, conducting vulnerability testing of AI models, and adhering to security-by-design principles. Applying DevOps principles to AI development, often referred to as machine learning operations (MLOps), helps ensure continuous security integration.
Continuous Monitoring and Evaluation of AI Models
Deployed AI models require continuous monitoring to ensure their ongoing effectiveness and to detect any signs of compromise or degradation. This includes monitoring for data drift, concept drift, and adversarial attacks. Regular evaluations help maintain model integrity and performance in a dynamic threat environment.
Best Practices for Responsible AI Adoption
Responsible AI adoption means maximizing benefits while mitigating risks, emphasizing human collaboration, and adhering to ethical principles. This involves thoughtful deployment and continuous learning.
Prioritizing Human-AI Collaboration and Augmentation
AI should augment human capabilities rather than replace them. Security teams must retain ultimate oversight, using AI as a powerful tool to enhance their decision-making and efficiency. Human analysts provide critical contextual understanding and intuition that AI systems currently lack.
Government guidance reinforces this approach. The joint agencies' guidance recommends deploying AI agents incrementally, starting with clearly defined low-risk tasks, granting least-privilege access, and keeping humans in the loop to approve high-impact actions.
Establishing Clear Ethical Guidelines and Policies
Organizations must develop and adhere to clear ethical guidelines for the development and deployment of AI in cybersecurity. These guidelines should address issues such as data privacy, algorithmic bias, transparency, and accountability. Ethical frameworks ensure that AI is used in a manner that aligns with an organization's values and societal expectations.
Integrating AI with Existing Security Ecosystems
AI solutions should not operate in isolation but instead integrate directly with an organization's broader security ecosystem. This creates a more cohesive and powerful defensive posture.
AI should augment existing security tools, including Security Information and Event Management (SIEM) systems,firewalls, and endpoint detection and response (EDR) platforms. This integration allows AI to enrich data, automate responses, and provide deeper insights across the entire security stack. A unified approach maximizes the value of AI investments.
How Can Organizations Measure the Effectiveness of AI in Cybersecurity?
AI cybersecurity investments should be evaluated using measurable security outcomes rather than adoption levels alone.